Security and privacy
Your code, your data, your choice.
Flowmark works with the core of your IT landscape: integration code and operational data. Here is how we protect it, and which choices you make yourself.
Our principles
Confidentiality, integrity and availability
Information security is not a separate part of Flowmark. It is the foundation the platform is designed on.
Confidentiality
Only people who need access get access. Sensitive fields are masked before any analysis runs.
Integrity
Flowmark reads your code and monitoring data to provide insight and does not change your integrations.
Availability
Flowmark can be hosted with the provider of your choice. Availability depends on that provider, or on your own infrastructure when you run on-premises.
Certification
ISO/IEC 27001 certified
Our information security management system is certified to ISO/IEC 27001, assessed by BSI.
Hosting
You choose where Flowmark runs
Every organisation has its own requirements for data location and control. That is why Flowmark is available in three forms.
Public cloud
Run Flowmark with a major cloud provider, such as Microsoft Azure.
European cloud
Hosting with OVH, a European cloud provider.
On-premises
Flowmark runs in your own environment, under your own control.
AI and language models
You decide which language model sees your code
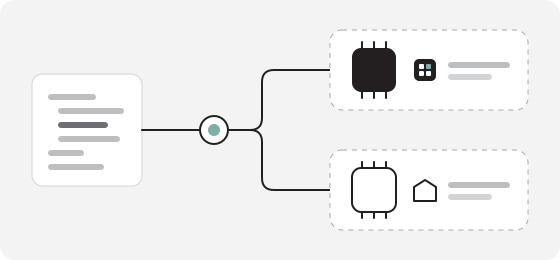
Flowmark uses a language model to analyse integration code and business rules. Which model that is, is up to you.
- Local language model via Flowmark. Optionally, Flowmark hosts a local model for your analysis.
- Your own language model. Connect the model your organisation already uses or has approved.
Supported models: Claude, OpenAI, Google and open-source models.
Security strategy
The pillars of our security
How we protect the platform and your data, from the integration flows to access.
Prevention
- Automated vulnerability scanning of integration flows
Compliance
- ISO/IEC 27001 certified
Infrastructure
- Hosting with the provider of your choice or on-premises
- Network, perimeter and DNS security
Customer data protection
- Encryption in transit (TLS) and at rest
- Logical tenant separation
Backup and recovery
- Disaster recovery scenarios tested annually
- Production databases backed up daily
Identity and access
- Role-based access control
- Multi-factor authentication (MFA) by default
GDPR
Privacy and the GDPR
Flowmark mainly processes technical data: integration code, configuration and monitoring data. Below is what we process and how.
What data we process
From website visitors: IP address, browser and device data, page visits via cookies and what you enter in the contact or demo form. From customers: contact, contract and invoicing details and the account and log data of administrators. We do not ask for special categories of personal data. Data you process in the Flowmark platform is processed by us as a processor on your behalf.
How and where we store data
In data centres within the European Economic Area (EEA), encrypted in transit and at rest. Transfers outside the EEA only take place on the basis of an adequacy decision, such as the EU-US Data Privacy Framework, or the European Commission's Standard Contractual Clauses.
Who has access
Staff only have access to data they need for their work. Processors, such as our hosting providers OVHcloud and Microsoft Azure (platform) and Vercel (website), work under a data processing agreement. A current list of sub-processors is available via privacy@flow-mark.ai. We do not sell personal data.
Agreements and contact
We process personal data in line with the GDPR and work with an ISO 27001 certified management system. Send questions about privacy or your rights to privacy@flow-mark.ai. Our Data Protection Officer can be reached at dpo@cronos.be.
This is a summary. The privacy statement is leading.
Documents
Want to know more?
Privacy statement
What data we process, why, and which rights you have.
Read the statementCookie statement
Which cookies we use and how you manage your choice.
Read the statementISO/IEC 27001
Our certified information security management system.
Go to certificationSecurity questions
We are happy to answer questions from your security, privacy or procurement team.
security@flow-mark.aiFAQ
Security questions
Yes. Our information security management system is ISO/IEC 27001 certified.
You decide: in a major public cloud, in a European cloud (OVH) or on-premises in your own environment. Availability depends on the provider you choose.
You choose. Optionally use a local language model hosted by Flowmark, or your own model. Supported are Claude, OpenAI, Google and open-source models. Your data is not used to train models.
All communication with Flowmark is encrypted with TLS, and data is stored encrypted. Customer environments are also logically separated from each other.
Access is role-based, and multi-factor authentication (MFA) is on by default.
Questions about security?
Our team is happy to answer questions from your security, privacy or procurement team.